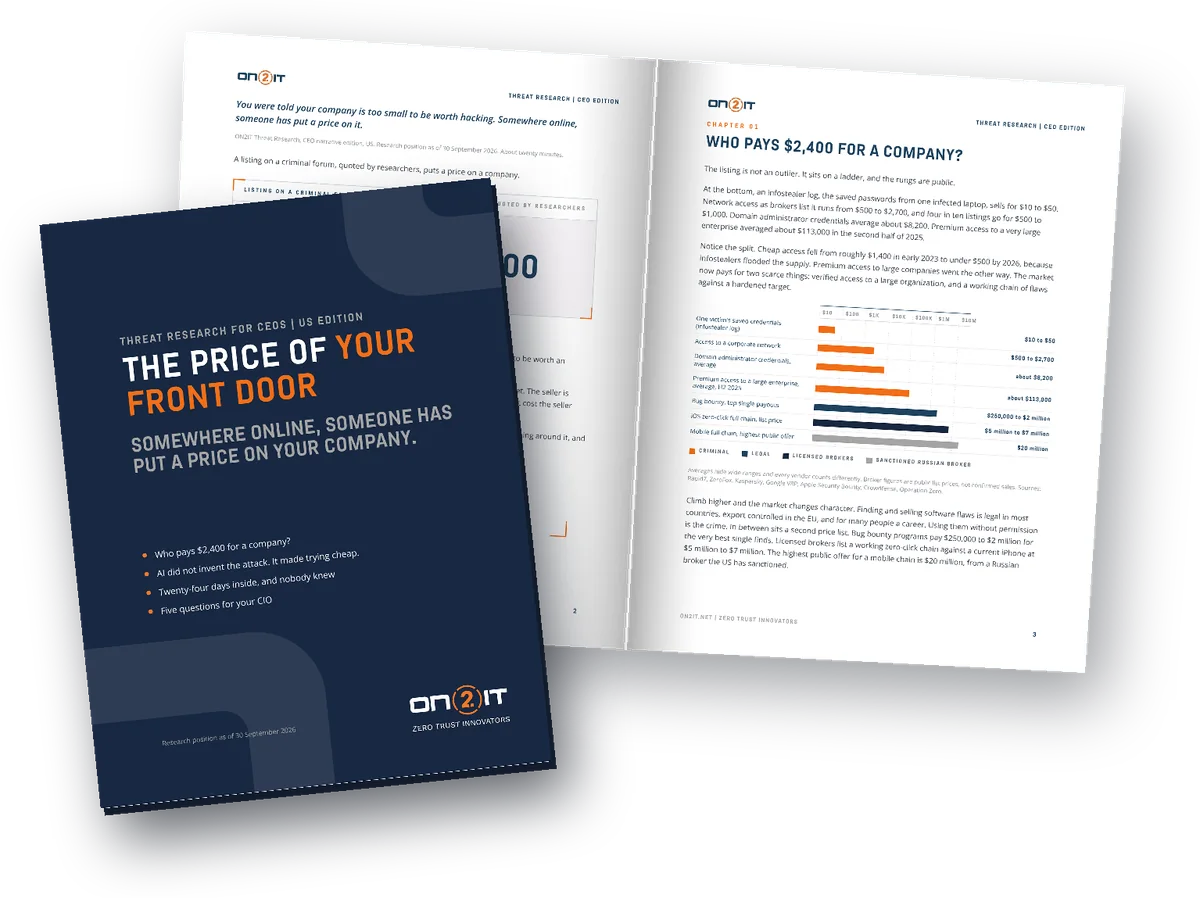


The price of your front door.
You were told your company is too small to be worth hacking. Somewhere online, someone has put a price on it.
Threat research report
CEO edition, United States
- 12 chapters
- About 20 minutes
- Research as of 30 Sep 2026
Every claim sourced
Anthropic, Microsoft, CISA, Mandiant, Palo Alto Networks Unit 42, CrowdStrike, Verizon, Chainalysis and others.
Zero Trust pedigree
ON2IT advised on the 2022 NSTAC report to the President on Zero Trust and Trusted Identity Management.
Not $2.4 million. $2,400.
A US manufacturer, $180 million in revenue, 400 endpoints. Full domain administrator access through a stolen VPN login, listed on a criminal forum. The asking price: $2,400. Not $2.4 million: two thousand four hundred dollars.
This company was not too small. It was cheap.
The seller is not selling secrets. Nobody has opened a single contract yet. The seller is selling the door: a password that still works. The usual buyer is an extortion crew, and for them $2,400 is small change next to a ransom.
AI did not invent the attack. It made trying cheap.
On 10 September 2026, Anthropic published a 154-page report on attacks it disrupted on its own AI models. Its conclusion: AI cut the cost of each campaign while the payoff stayed the same. Targets that were once not worth the effort are worth it now.
“We’ll patch it” is not a plan either. This year, the Microsoft Defender malware scanning engine had a public exploit and no fix for 22 days. Citrix NetScaler gateways at the edge of dozens of networks were exploited for up to 24 days before a patch existed, mostly unnoticed.
The full report shows who buys doors like yours and what they pay. It ends with five questions to ask your CIO this week, so you know what still protects you when there is nothing to install.
What the full report gives you.
Unlock the full report
The full story in about twenty minutes, written for CEOs. Free, to read online.
Unlock the full report